

People in security spend their day in dashboards, tickets and log queries. I spend a good chunk of mine working out how to explain a ransomware gang’s toolkit with a camera, some lighting and a script.
My job is making videos about threat research at Sophos. Video has always been a huge passion of mine, right alongside cybersecurity, and for a long time those two things lived in separate boxes. One was the day job. The other was the thing I did on evenings and weekends. Getting the chance to host The X-Ops Brief full time is a dream come true, and I still find it a bit strange saying that out loud.
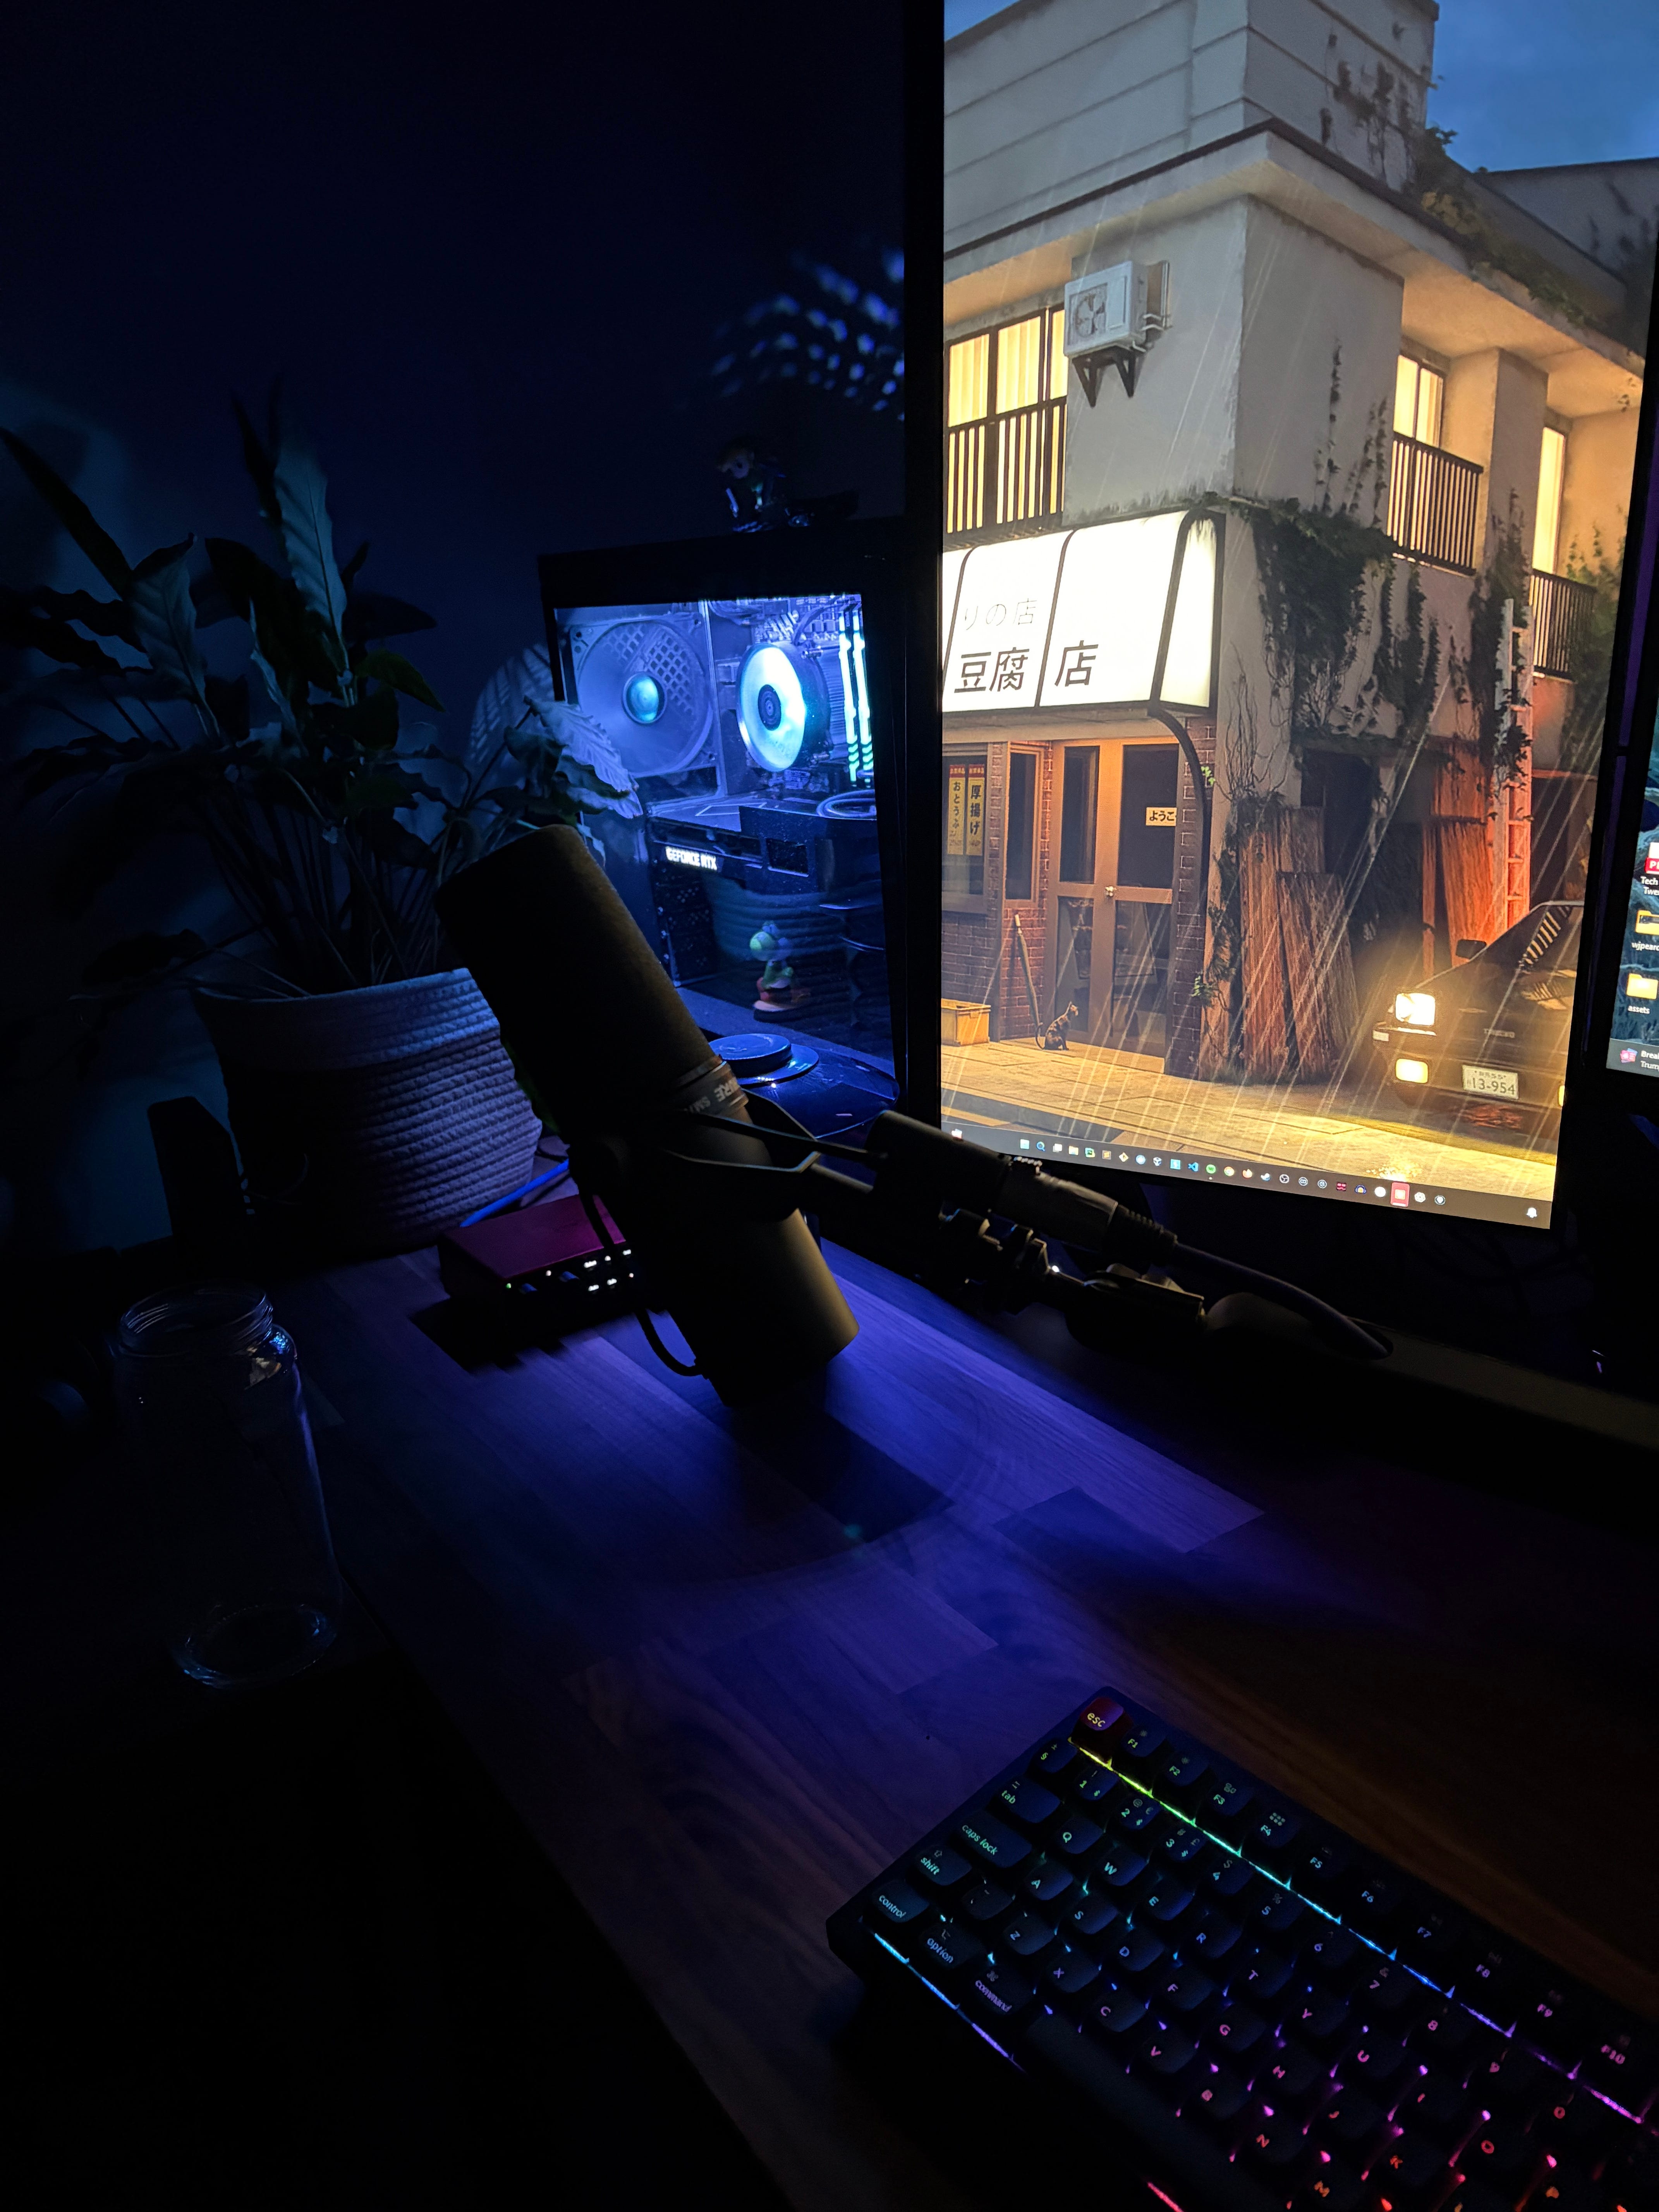
I’m telling you this for a reason, and it isn’t just to show off the cool mic I got
A lot of you reading Cyber Notes are just getting started. Cloud students, career changers, people building their first home lab project. And a question I get in my DMs almost every week is some version of “do I need to follow the exact standard path to get into cyber?”
You don’t. I have an art degree. That’s not the CV most people picture when they think “security engineer”, and yet it’s the exact thing that led me to a role nobody would have put on a careers poster. Security needs people who can build, break and defend things. It also needs people who can explain what’s going on to everyone else. Your odd mix of skills might be your biggest advantage.
If you’re studying for a cloud or security cert, watch it with that lens. Every technique mentioned is something you can look up, map to MITRE ATT&CK and then try spotting in your own test environment. That’s a free project idea right there.
👉 Watch the new episode of The X-Ops Brief:
If you enjoy it, hit reply and tell me which attack you’d like me to break down next. I read every one.
W J Pearce - Cyber Notes